Deepfake Detection: Verify the Source, Context and Your Reaction
Visual clues are fading as AI improves. Check where a clip came from, seek corroboration and treat detector results as a reason to investigate.
Latest stories
Visual clues are fading as AI improves. Check where a clip came from, seek corroboration and treat detector results as a reason to investigate.
A survey finds widespread chatbot use among young people, while a separate study links some patterns of AI use with poorer well-being.
AI tools make convincing fake sites and accounts easier to create. Check URLs, trace claims, and treat emotion driven posts and detectors with care.
AI generated posts, fast moving feeds and weaker moderation make verification harder. A deliberate pause can help people assess what they see.
A wave of late 2000s nostalgia is giving younger users a shared language for hope, even as the era’s promise looks more complicated in hindsight.
TikTok’s separate Shop app brings product videos, livestreams and checkout together, testing whether discovery can turn into a dedicated shopping habit.
A California measure would restrict autoplay and personalized feeds for users under 16. The companies say those features are part of how they deliver content.
A threat actor used Hermes Agent and DeepSeek V4 to coordinate intrusions and prepare other schemes, showing how AI can widen one operator’s reach.
A customized Cairn framework used Chinese AI models to pursue targets autonomously, confirming access or data retrieval at 10 organizations.
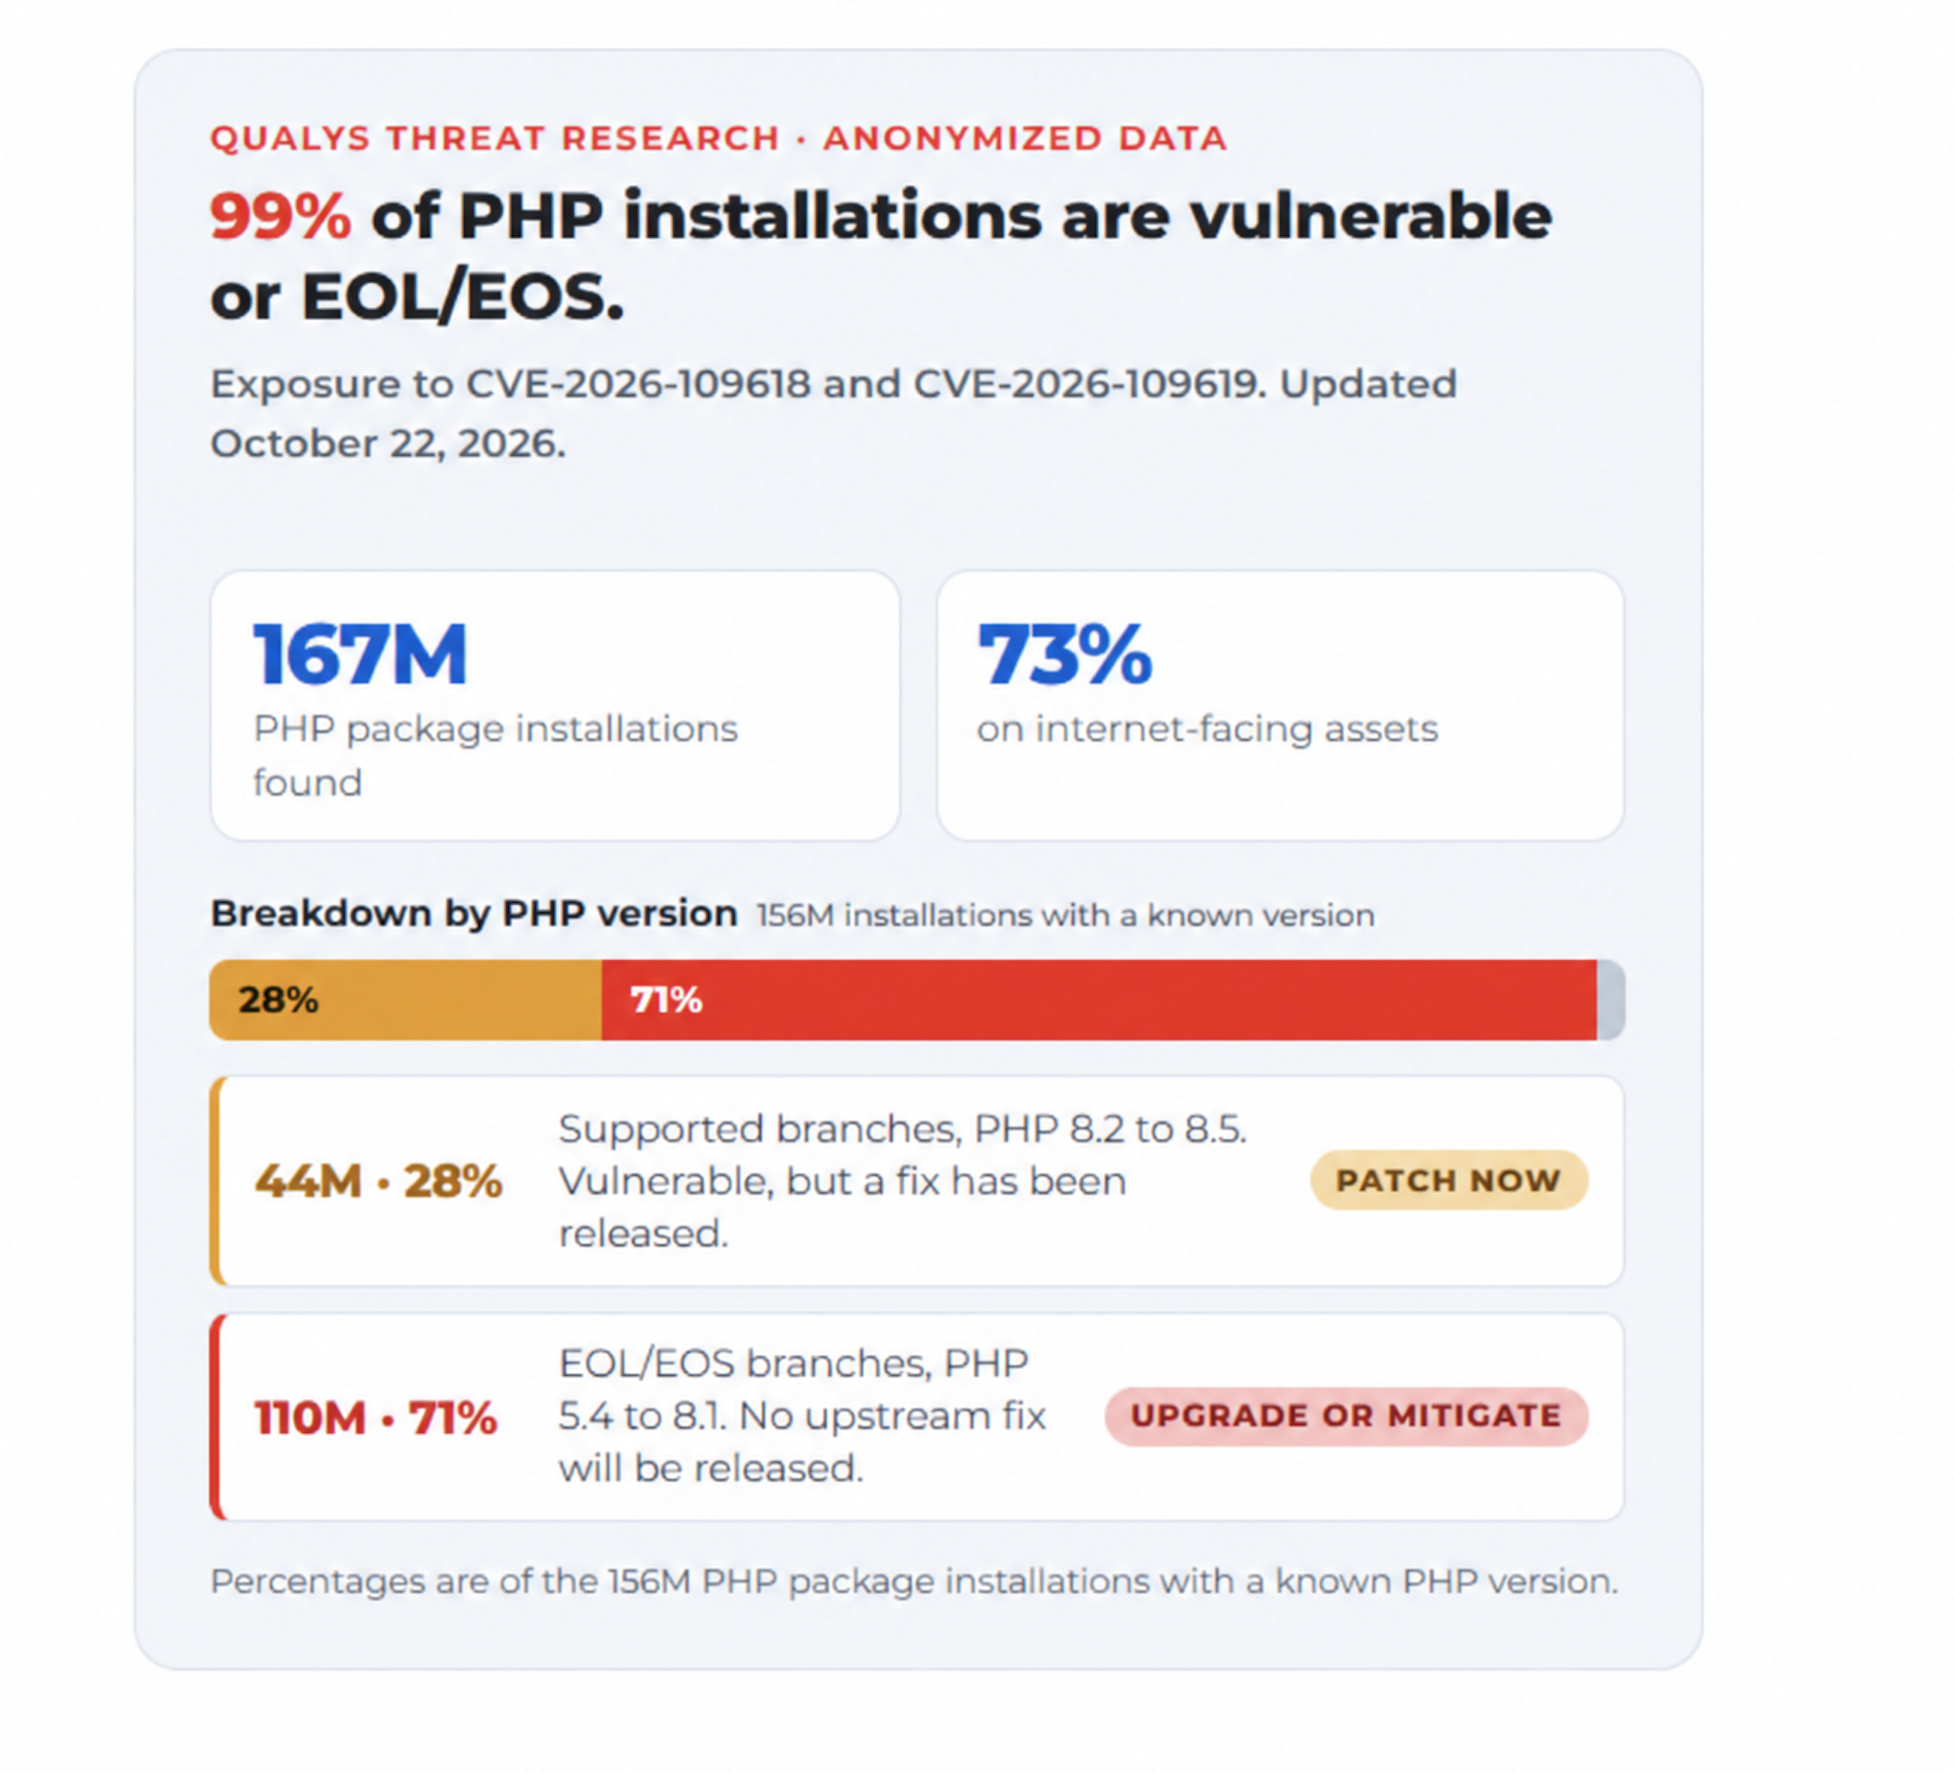
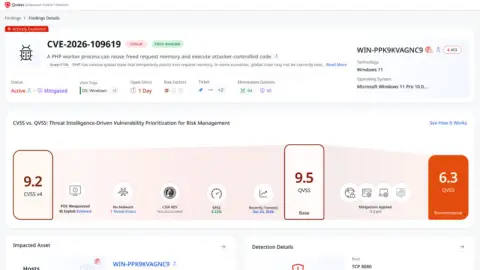
Two PHP flaws enable unauthenticated code execution and memory disclosure. Find exposed runtimes, apply fixed builds, and verify every worker.
BlueHammer requires a user-level foothold and specific host conditions. Defender 4.18.26030.3011 closes the vulnerable path; safe validation checks whether it’s...
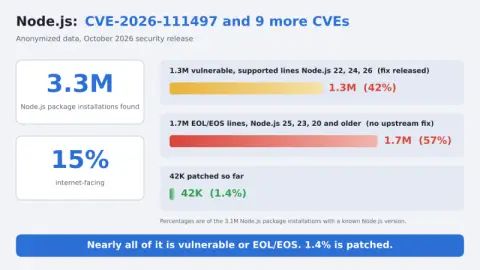
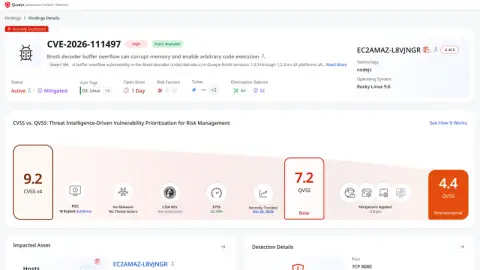
Node.js fixed 10 runtime flaws, including a Brotli memory write issue. Teams must upgrade supported versions and locate runtimes embedded in apps and containers...
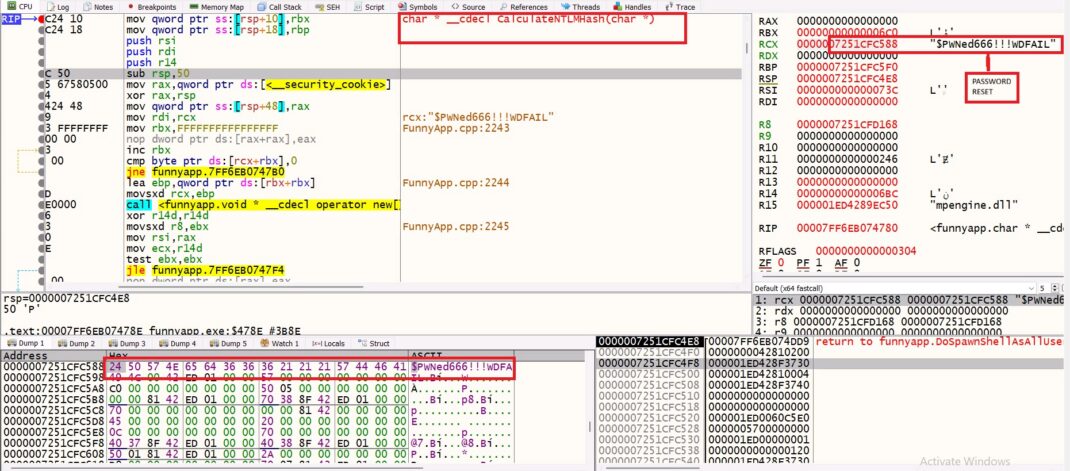
Use configuration changes, reachability checks and existing security tools to reduce PHP2Shell exposure while teams patch affected systems.
Node.js fixes a Brotli flaw in 22.23.4, 24.22.1 and 26.12.1. Inventory, interim controls and service restarts help reduce exposure while upgrades roll out.
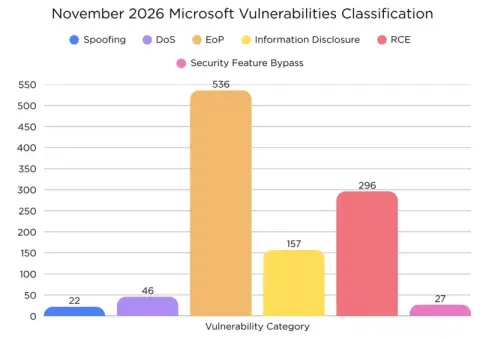
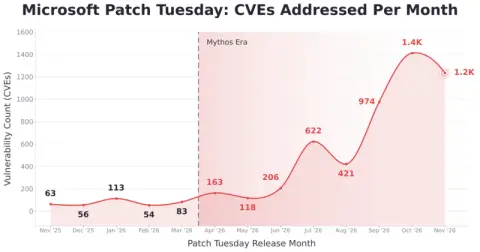
Microsoft fixes 1,235 vulnerabilities, including one exploited in the wild; Adobe patches 63 flaws across six products.
November’s 1,252 CVEs call for early exposure checks, patch reliability review and staged deployment with mitigations when updates fail.